AI can make crisis communication faster, smarter, and more efficient. But how safe is it, really, to use AI when sensitive information is involved? And does that mean the solution is to simply avoid using AI altogether for now? According to AI specialist Maarten Sukel, that is precisely one of the biggest mistakes organizations can make.
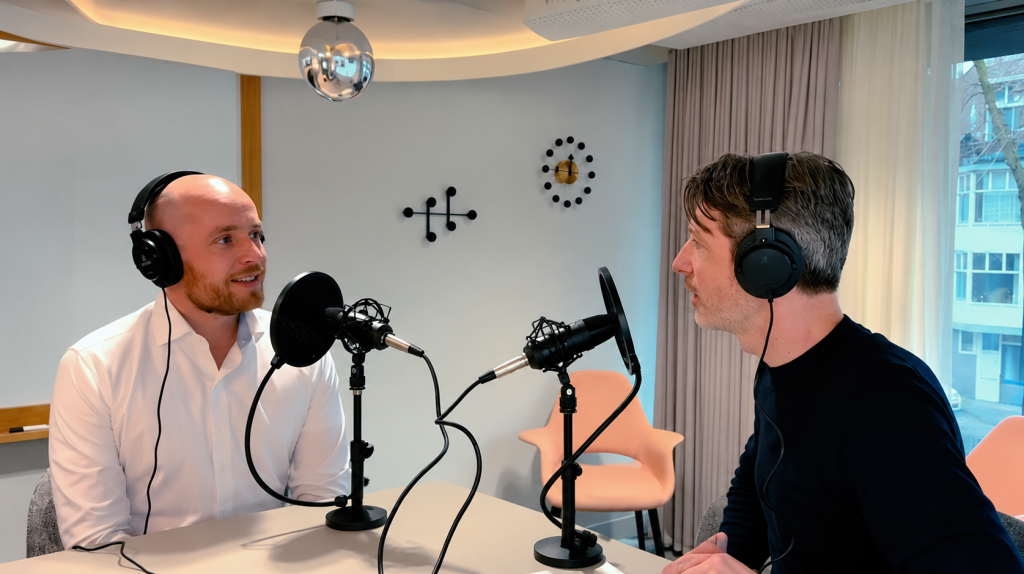
Tom Compaijen, founder of FirstRing, sits down with Maarten Sukel, AI specialist and CTO of FirstRing. Together, they discuss the risks of AI, the differences between well-known AI systems, and how organizations can use AI responsibly during a crisis.
No one admits it, but everyone does it
Many organizations are struggling with the use of AI. Employees are increasingly discovering how useful tools like ChatGPT can be, while organizations are still in the process of establishing their policies. Sometimes, the use of AI is even banned altogether. But does that mean employees aren’t using it?
According to Maarten, absolutely not. During presentations at banks and government organizations, he regularly asks who uses a personal account for AI. Virtually no one raises their hand. But afterward, people still come up to him to admit that they actually do it on the sly.
And that, he says, is precisely where the risk lies. When employees use AI tools on their own, an organization has virtually no insight into what information is being shared, where that data ends up, and what security settings are being used.
Isn’t doing nothing actually much more unsafe? According to Maarten, it is. Organizations are better off making a conscious choice to establish a well-designed AI environment, with clear guidelines on its use. Because not having a policy doesn’t mean AI isn’t being used. Above all, it means you have less control over it.
What actually happens to the information you feed into AI?
One of the biggest concerns surrounding AI is that confidential information could be leaked. This is especially true during a crisis, when sensitive business information, personal data, or unconfirmed facts may be shared.
Maarten draws an interesting comparison with email. When you send an email, that information also goes to a server. We hardly even think about that anymore. If you first use ChatGPT to improve that same text, you’re adding an extra system to the mix. And every additional system with which you share information brings new risks.
That doesn’t mean AI is inherently unsafe. However, the environment you use does matter. With certain consumer versions, the data you enter may be used to further train AI models, depending on the settings and terms and conditions. With business solutions, different arrangements can be made regarding this.
But a paid subscription alone isn't enough. The settings, access rights, and agreements with the provider must also be properly arranged. That's why Maarten thinks it's wiser to make AI available centrally within an organization, rather than having each employee set up their own account.
So is Microsoft Copilot automatically the safe choice?
Many organizations choose Microsoft Copilot because they already use Microsoft products. That feels familiar—and therefore safe. But according to Maarten, it’s not as straightforward as it seems.
Depending on the configuration and access rights, Copilot can use information from sources such as SharePoint and other connected Microsoft environments. This makes it a powerful tool, but it also requires that those access rights be properly configured. After all, if employees have access to documents they shouldn’t actually be able to view, an AI assistant can exacerbate existing problems.
The same applies to where data is stored. More and more organizations are opting for European servers, based on the assumption that their information is safer there. But Maarten has a caveat here as well. After all, data can be copied or accessed from other countries. So a server’s location doesn’t tell the whole story about its security. The question is not just where your data is stored, but above all who has access to it and how it is protected.
What can and can't you share with AI during a crisis?
During a crisis, this discussion suddenly becomes very real. Suppose a serious incident occurs within an organization. The crisis team has information that has not yet been made public, but an initial communication strategy or statement must be drafted quickly. What information can you safely share with AI in that situation?
Tom explains how he handles this himself: information that is already public—for example, through news media—can generally be used without much concern. But when it comes to non-public information, things get more complicated. Think of personal data, the names of those involved, information that could jeopardize a criminal investigation, or confidential business information.
According to Maarten, professional AI environments with robust technical and contractual safeguards offer many opportunities for secure data processing. Still, it’s wise to carefully consider what information you actually enter. After all, just because something is technically possible doesn’t mean it’s necessarily necessary.
And especially during a crisis, when time is of the essence, it helps if organizations have already reached agreements on this in advance.
Security goes beyond simply protecting data
Another important point Maarten raises is that security isn’t just about privacy. During a crisis, an AI system must, above all, be reliable and available. After all, what good is a highly secure tool if it doesn’t work precisely when you need it most?
AI models rely on complex technical infrastructure, and outages can never be completely ruled out. Therefore, the development of FirstRing takes into account the availability of various AI models, so that the platform is less dependent on a single provider.
In addition, the quality of the responses is also important. AI can still make mistakes or invent information—a phenomenon also known as “hallucinating.” In crisis communication, such errors can have serious consequences. After all, a false assumption or an inaccurate statement can further complicate the situation.
That is why human oversight remains essential. AI can assist in analyzing information, determining a course of action, and drafting communications, but the crisis communications professional must continue to assess whether the results are accurate. That person knows the organization, its sensitivities, and the actual situation.
The most important question isn't whether AI is safe, but how to keep it safe
Perhaps the most important message is that security is not a one-time decision. An AI system that is well-secured today will not remain so on its own. Technology changes, vendors continue to develop their products, and new risks emerge. That is why organizations must continue to evaluate and improve their systems and security measures.
Maarten therefore turns the usual question on its head. Instead of simply asking whether an AI system is safe, organizations should primarily ask themselves: How do we ensure that it remains safe?
This calls for conscious decisions, clear agreements, and constant attention to safety. But above all, it requires a willingness to actually start working with AI. Because while organizations continue to debate the risks, employees are often already using it.
And that brings us back to Maarten’s most important piece of advice: don’t put off making decisions indefinitely. Because, in his view, the biggest mistake organizations can make is failing to make a decision at all.
Working safely with AI doesn't start with avoiding the technology, but with taking responsibility for how you use it.